 ASEC
Autonomy secured
the hard way
We get in first, so adversaries can't. You see every gap before they do, and take control of your security.
Trusted by
Most of our work is under NDA, so this is the short list.
The argument
Two clocks are running. Only one is yours.
The exposure window is how long a weakness stays reachable, from the moment it exists to the moment it is genuinely closed. It predicts both outcomes that matter: whether you get breached, and how badly it lands. Every other number the industry counts is a proxy for it.
Median time from initial access to handing that access to another crew, down from more than eight hours in 2022.
Mandiant M-Trends 2026Average breakout time in 2025: intrusion to lateral movement. The fastest observed was 27 seconds.
CrowdStrike Global Threat Report 2026Median time from a vulnerability being published to it being confirmed exploited in the wild. It was 8.5 days the year before.
Rapid7 Global Threat Landscape Report 2026Global median dwell time in 2025, how long an intruder sat inside before anyone noticed. It rose from 11.
Mandiant M-Trends 2026Median dwell time when somebody outside the organisation was the one to break the news. It rose from 11.
Mandiant M-Trends 2026Average breach lifecycle, identify through contain. Organisations that found it themselves saved roughly $900,000.
IBM Cost of a Data Breach 2025Twenty-two seconds against fourteen days. No count of open criticals closes that gap. Shortening your side does. So we keep the same clock we ask you to keep, and criticals reach you the day we prove them, with a reproduction and a fix.
Open source
Open-source projects
github.com/nicholasaleks → 821
Damn Vulnerable Drone
Intentionally vulnerable drone hacking simulator on the ArduPilot/MAVLink stack. A full lab for hands-on drone security.
 352
CrackQL
GraphQL password brute-force and fuzzing utility for testing API authentication at scale.
SiKW00F
Drone SiK radio detection and MAVLink telemetry eavesdropping toolkit.
Infected Drones
A collection of vulnerabilities and exploits against modern ground control stations.
What we do
Full-stack offense
Drone and robotics testing, adversarial assessments, security consulting, incident response, and the ASEC platform.
Experience
More than a decade in business.
Member of
Who breaks it
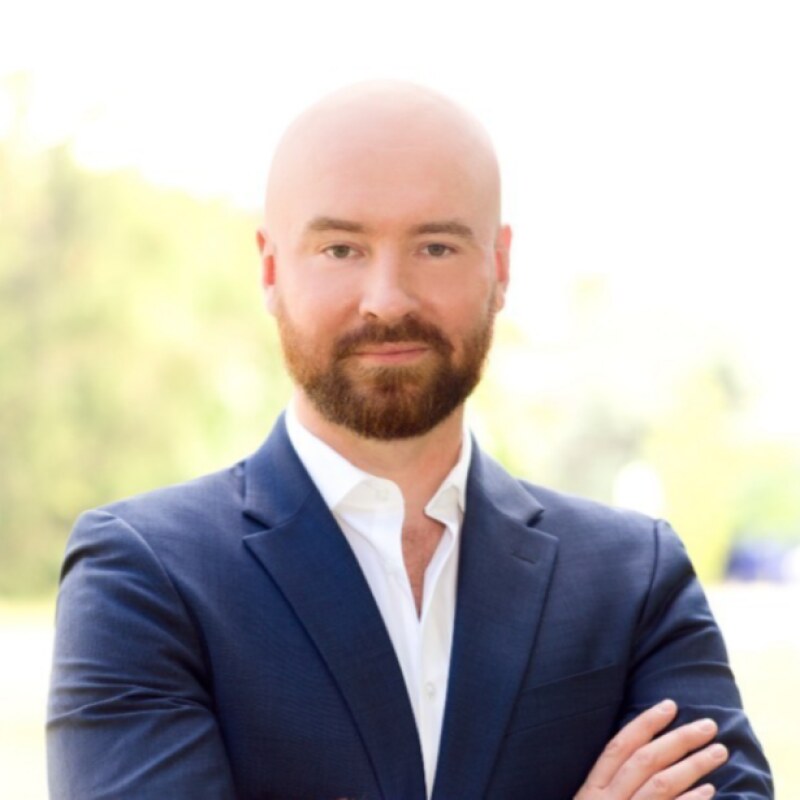
Nick Aleks
Founder & CEO
Nick Aleks is a security engineer, researcher, and the founder and CEO of ASEC. He's led security at some of the biggest names in fintech, including Wealthsimple and Robinhood, and now heads security at Dominion Dynamics. Over ten years he's broken into websites, APIs, safes, locks, cars, drones, and smart buildings, and he trains the next wave of hackers on advisory boards at George Brown and the University of Guelph.
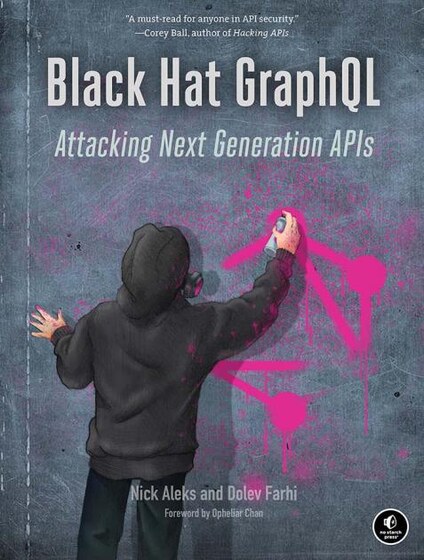
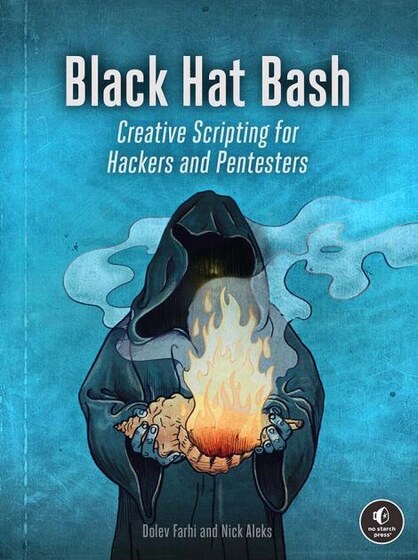
He also co-wrote the books the industry trains on.
 Founder of DEF CON Toronto, with more than 3,000 members.
The ask
Your exposure window is ticking.
Tell us what you're building and what you're worried about. You'll hear from an operator, not a sales team, within one business day.
Call us
Business hours, Eastern TimeFind us
18 King Street East, Suite 1400
Toronto, Ontario
M5C 1C4